Why is ignoring package-lock architectural suicide?
- May 2026 |
- 04 Mins read
There is a silent error that lurks in many modern repositories and is often passed off as good development practice: adding the package-lock.json file to the gitignore. It is most common in Node.js projects like React, Angular, and Next.js, where npm generates this file automatically on every install. The argument is straightforward and, on the surface, reasonable. If the dependencies are already declared in the project’s main configuration file, adding another massive file dense with hashes to version control seems like nothing but unnecessary noise in the diffs. This belief, however, is not just technically wrong. It represents a concrete risk to product stability, as it silently dismantles the foundational principle on which any reliable development environment is built: environmental determinism.
The problem hidden in version symbols
To truly understand the scope of the issue, one must first understand how package managers interpret dependency declarations. When a library is defined with the classic caret prefix, the system is being granted explicit permission to download newer versions as soon as they are published by the original authors. This behavior is by design, intended to simplify the receipt of bugfixes and security patches, but it introduces a variable that most developers tend to underestimate: every installation performed without a lock file becomes potentially different from the previous one, with outcomes that are impossible to predict in advance.
The problem is amplified when considering the depth of the dependency tree. A moderately sized project may have dozens of direct dependencies, each pulling in dozens more in a cascading fashion. Without a mechanism that pins the entire hierarchy precisely and in a versioned form, the actual composition of installed packages depends on the exact moment the installation command is run. The developer who worked on the code two weeks ago and the one who clones it today may end up with concretely different dependency trees, despite starting from the same configuration file.
The ghost bugs of deployment
This divergence is the primary cause of those hard-to-reproduce failures that appear out of nowhere during a production release. A minor update to a third-party library, perhaps an indirect dependency the team did not even know existed, can introduce a regression that breaks the entire build in the production environment while everything appears to work perfectly in local. In these cases, the problem does not lie in the application code written by the team, but in the variability of the underlying environment that nobody thought to make explicit and versioned.
In a professional architecture, the guarantee that the tested code is identical, bit for bit, to what is actually deployed is not an optional luxury. It is a fundamental reliability requirement, without which every release becomes an act of blind trust in a package ecosystem that changes continuously and has no obligation to notify us of its modifications. The most mature engineering teams know this well: environment reproducibility is the first line of defense against unexpected downtime, and the lock file is the simplest and most direct tool for ensuring it.
The invisible dimension of security
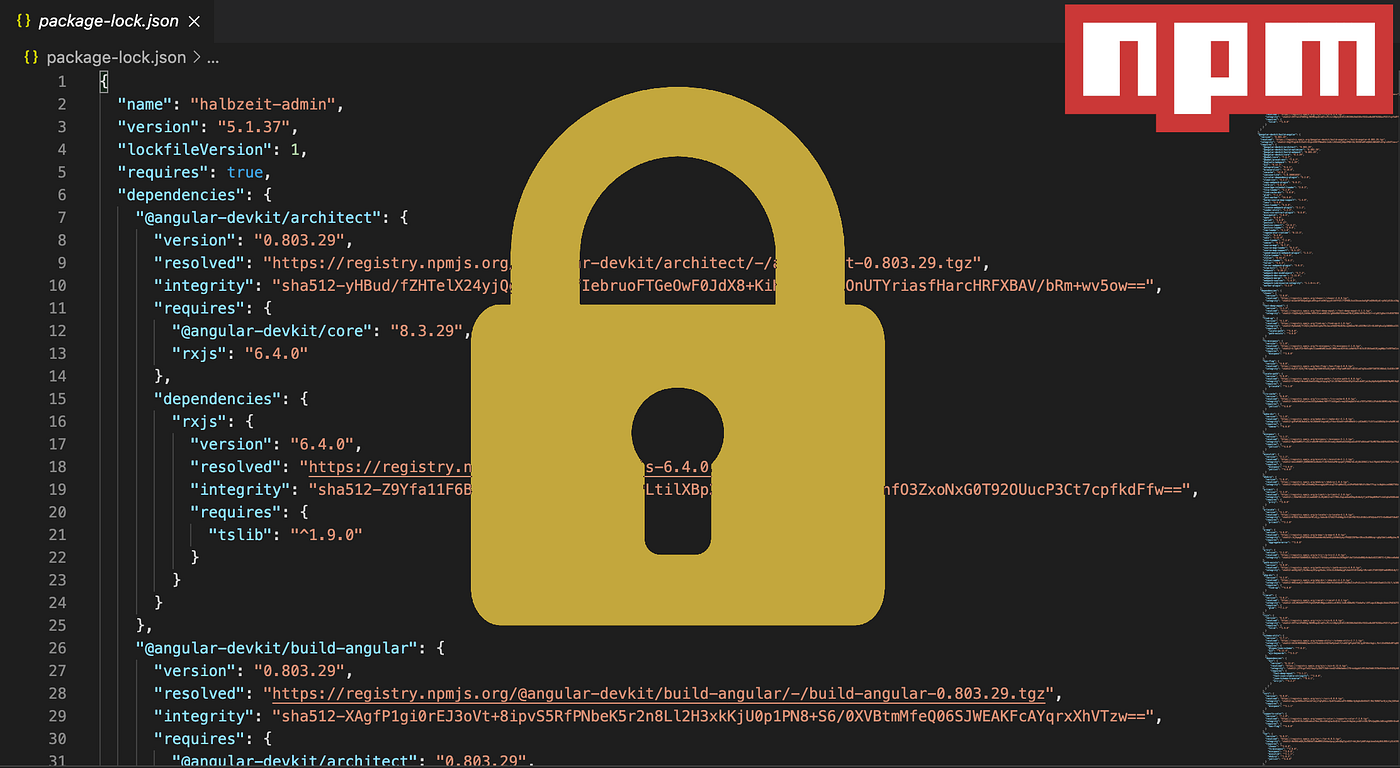
Beyond consistency across environments, the lock file fulfills a critical function in the field of information security that is often overlooked. Each entry it contains includes a cryptographic integrity hash that guarantees the downloaded package is exactly what was expected, without any alterations having occurred during network transit or within the package registry itself. This is a thin but essential shield against software supply chain attacks, a rapidly growing category of threats that aims to inject malicious code not into the project directly, but into its dependencies.
Attacks of this kind are particularly insidious because they tend to go unnoticed during normal development and code review phases. A compromised package that enters the dependency tree without an integrity check can propagate harmful code all the way into production without any automated test or manual review catching it. Ignoring the lock file means giving up this level of verification, leaving the infrastructure exposed to attack vectors that may not manifest until the damage has already been done.
From chaos to a deterministic workflow
The picture that emerges from this analysis is clear: the visual noise that a lock file generates in commits is a trivial price compared to the risks its absence carries. Managing this file correctly means making a precise transition, from an approximate and non-reproducible management approach to a deterministic workflow where the installation command does not introduce unexpected variables but guarantees continuity with respect to the environment already validated by the team.
In continuous integration pipelines, this principle translates into adopting specific commands that ignore generic version definitions and force the exclusive use of the lock file. This approach represents the established standard for ensuring that every build produced by automation is an exact replica of what the team developed and tested. Adopting it does not require a deep architectural rethinking, but simply the awareness that every decision about the execution environment carries consequences that propagate silently through the entire release chain, all the way to the end user.